
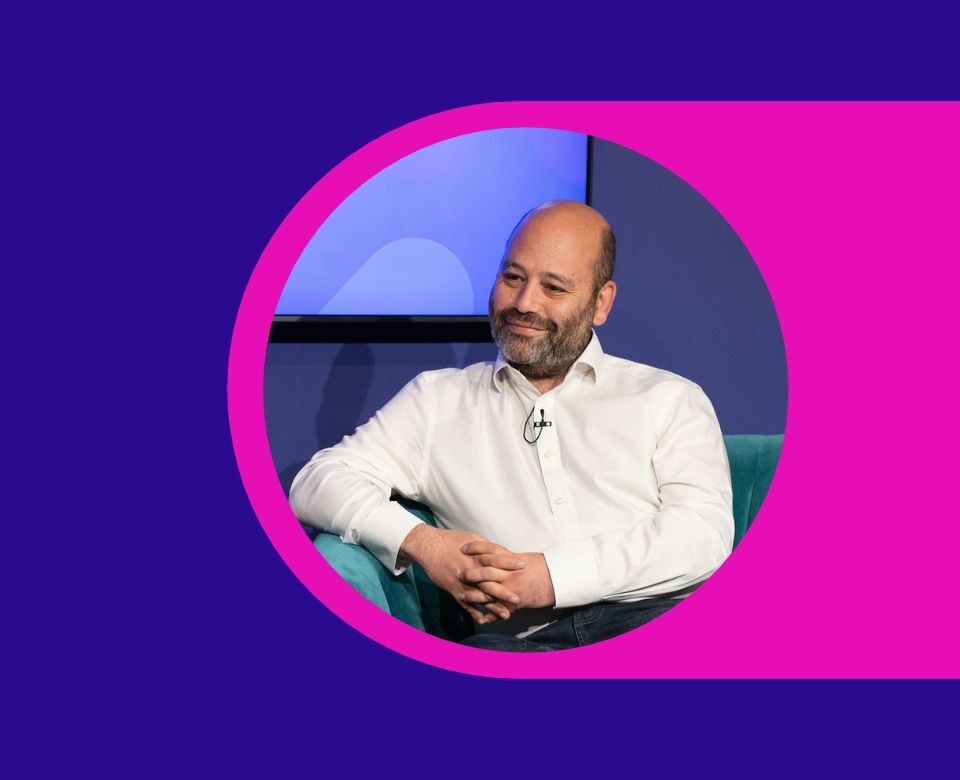
Leaders Profile: David Boda, Chief Security and Resilience Officer, Nationwide
Kani Talabani
Share this post


Leaders Profile interview with David Boda, Nationwide’s Chief Security and Resilience Officer
What does the life of a Chief Security and Resilience Officer look like in 2026? In this Leaders Profile interview with HotTopics, Nationwide’s David Boda recalls how his journey to security leadership was sparked from a young age.
Cybersecurity was not always destined to become David Boda’s career, but one university course was enough to set him on a path that would eventually lead to the upper, more senior levels of resilience and security leadership.
While completing his undergraduate degree, Boda encountered a cybersecurity course sponsored by Microsoft, one of the first of its kind at the time, and it immediately caught his attention. “That kind of set my journey off,” he explains, “Security, not so much resilience. I’ve kind of learned that on the job.”
He subsequently completed a Master’s at Royal Holloway, University of London, an experience that cemented his overall interest in the cybersecurity field.
“There’s so much to learn,” Boda says, “I love that there’s always something new to learn. It’s fast-moving and always expanding.” That appetite for learning still remains central to his approach today.
Now Chief Security and Resilience Officer at Nationwide, Boda has a remit extending beyond conventional cybersecurity. His role encompasses the organisation’s ability to respond to disruption, recover from incidents, and maintain the services its customers depend on.
Yet, speak to him about leadership for any length of time, and the conversation repeatedly returns to less technical: you guessed it, people.
From cybersecurity to operational resilience
Boda joined Nationwide in January 2023, describing himself jokingly as a “relative baby in financial services” compared with professionals who have spent their entire careers in the sector.
His move into resilience was less of a planned career pivot than an expansion of skills accumulated throughout his career. Leadership, finance, people management and resilience were, he says, among the things he learned “as you go”. At Nationwide however, bringing security and resilience closer is deliberate.
Operational resilience has risen up the agenda across UK financial services over the past decade. For Boda, there is a strong natural connection between protecting an organisation from cyber threats and ensuring it can continue operating when something goes wrong.
That means asking questions that extend beyond whether systems and data are protected:
- Can critical services continue during a major disruption?
- How quickly can they be recovered?
- Are dependencies understood?
- What happens if an important supplier suffers financial or operational distress?
- And when systems return, can transactions and services be reconciled correctly?
The complexity means much of Boda’s attention now sits beyond what might traditionally be considered the CISO remit. During a Studio discussion, he estimated around 60 percent of his time is spent on response, recovery and resilience.
No plan survives first contact
There is a contradiction at the heart of resilience planning.
Organisations need detailed plans for crises that, by definition, rarely unfold according to plan. Boda believes that the answer lies in building what he described as organisational “muscle memory”.
Plans matter because people under significant stress and pressure need structure; leaders must also recognise when circumstances require them to deviate from the playbook. Exercises should therefore become an important part of Nationwide’s resilience culture.
The organisation’s internal red team continually tests its own defences. It also carries out tabletop exercises involving subject matter experts and senior leadership and participates in exercises across the wider financial services industry.
“If you don’t do those things in peacetime, then you can’t expect someone to react well in wartime,” Boda says. The objective is simply not to prove that a documented process works, exercises expose teams to uncertainty and force them to make decisions without knowing what comes next.
There are boundaries. Boda says simulated phishing campaigns, for example, should not manipulate employees around sensitive issues such as remuneration, pay, or benefits.
The security leader who knows when to get out of the way
Ask Boda what he enjoys about cybersecurity and the answer is not simply its speed; it is the challenge.
“If it’s all fixed, maybe the job’s not much for me,” he jokes. Some challenges are deeply technical. Others involve culture or people: recognising someone with potential, helping them develop into a successor or working out how to shift behaviour across a large organisation.
For Boda, those problems can be equally rewarding. That philosophy influences how he behaves when incidents occur. Despite his own interest in getting involved, Boda believes senior leaders sometimes need to resist the temptation to take control.
“We built up a good team,” he says. “Even when we do have incidents, I feel relaxed about not changing my leadership style, not being directive, and taking a step back and letting them take the reins.”
There are situations where an incident becomes serious enough to demand more direct leadership. But intervening unnecessarily can deprive people of the experience they need to develop. “You’ve got to give people the experience, otherwise how are they going to grow themselves?”
The skill lies in recognising the difference between a genuine impending “car crash” and a situation where someone can make a mistake without catastrophic consequences. Boda calls it allowing people to “fail safely.”
Experience makes that judgement easier. A leader can provide autonomy while remaining close enough to intervene when necessary. The alternative, he argues, creatives two problems: a demotivated team and an exhausted leader.
And while protecting an organisation from cyber attacks provides obvious satisfaction, Boda says watching someone else develop is even better. “It’s far more rewarding to see someone succeed and develop and grow in their own career.”
How to stop being the department of ‘no’
The stereotypical security function says no. Boda’s first piece of advice for changing this reputation is uncomplicated: “Don’t say no”. But that does not mean security leaders should go and approve every request.
Instead, they need to explain why a particular decision has been made, understand the other person’s perspective and remain willing to have their own thinking challenged. “Take the extra few moments to explain the rationale,” he says.
Sometimes, another perspective may even change the security team’s original position. The goal is to build trust rather than enforce compliance through authority alone. At organisational level, Boda advocates a regular “heartbeat” of storytelling and interventions that keeps security visible without expecting one piece of content to resonate with everybody.
After all, he readily admits that for much of an organisation, security can appear “quite a dry, boring subject”. Security leaders therefore need to meet people where they are. That same principle applies in the boardroom.
Boda sees the security leader as a trusted adviser to the organisation, someone capable of translating technical concerns into questions about investment, risk, customers and business outcomes.
Reporting lines, in his view, matter considerably less than the ability to create credibility. “It’s about whether you’re able to understand the business,” he told a Studio audience, “I’m a trusted advisor to the business.”
Boda knows that getting there takes time, and it also requires relationships to exist before difficult conversations happen and an ability to tell compelling stories about why security matters.
Cyber expertise belongs in the boardroom
The relationship between security leaders and boards works both ways.
Boards should be equipped to challenge security management rather than simply receive updates from it. Financial services may be relatively mature in this respect, but Boda believes there remains a wider shortage of cyber expertise among non-executive directors.
“If it’s true to say that cyber is one of the biggest non-financial risks that most organisations face, then really they should have cyber expertise in the room so they challenge management and ask probing questions.”
That expertise does not necessarily require another executive director. An advisor or non-executive with appropriate experience can help board members ask better questions and determine whether management’s decisions are reasonable and appropriate.
“If you don’t educate yourself to a degree internally, then how can you look people in the eye and say you’re making the right decisions for the business?”
AI, automation, and keeping humans in the loop
The rapid development of AI makes curiosity and internal expertise even more important.
Boda sees automation becoming increasingly significant in cybersecurity particularly where organisations are defending themselves against attackers who are themselves able to operate at machine speed. But AI does not eliminate the need for specialist knowledge.
Giving someone access to an AI tool does not automatically provide the expertise required to ask the right questions or access its answers. Someone without a background in vulnerability research, for example, may not know which prompts or problems will produce genuinely useful outputs.
For security leaders, the challenge therefore becomes twofold: use automation where it can reduce repetitive work and technical debt, while continuing to invest in the expertise required to use those tools intelligently. It also returns the conversation to people.
Boda points to the pressure placed on security professionals responsible for making high-stakes decisions in the middle of the night. Automation that removes unnecessary burdens can improve not only efficiency but also the human experience of working in security.

RELATED ARTICLES
Join the community
To join the HotTopics Community and gain access to our exclusive content, events and networking opportunities simply fill in the form below.
