
Share this post


Building an effective cyber resilience strategy? C-Suite execs need to rethink boardroom accountability
Discover how CEOs, CIOs and CISOs can build a cyber resilience strategy that strengthens business continuity, boardroom alignment and recovery readiness.
Cyber resilience has long been considered the responsibility of IT and security teams; as organisations confront increasingly sophisticated cyber threats, technology outages and mounting regulatory pressures, the conversation is now shifting from preventing disruption to ensuring the business can survive it.
How quickly can a business restore its critical operations, protect its people and maintain customer trust when preventative measures fail?
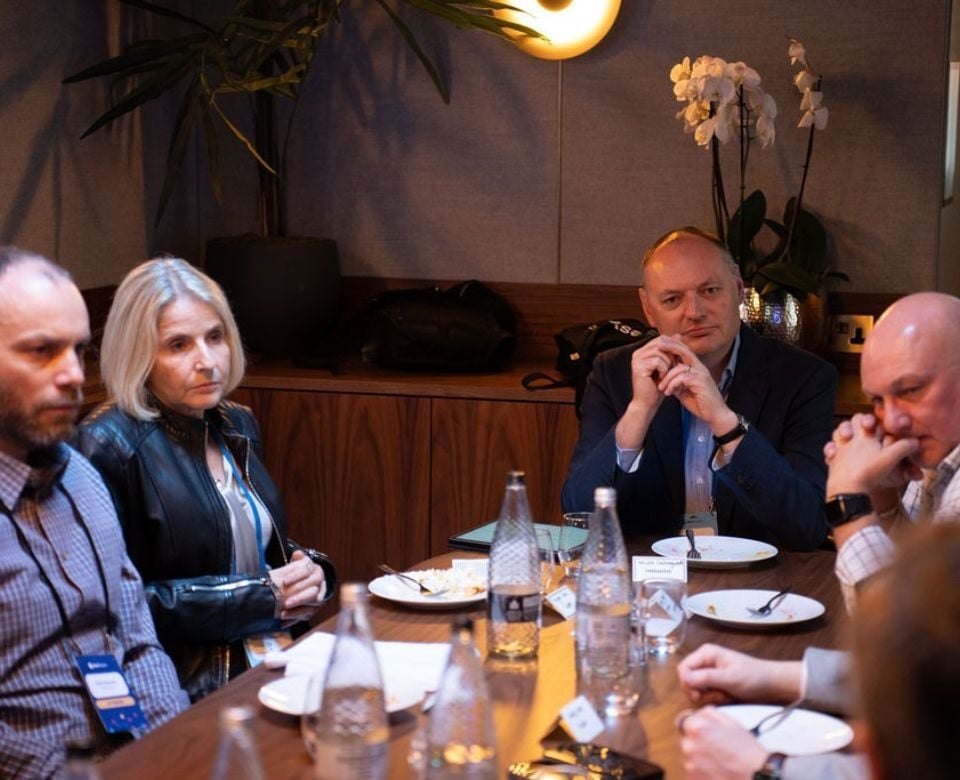
During a recent C-Suite Exchange, hosted in partnership with Absolute Security, senior technology and security leaders examined what it takes to build a cyber resilience strategy that extends beyond technical controls.
Cyber resilience strategy: A shared boardroom responsibility or an IT problem?
An opening poll revealed a divided picture of how organisations approach resilience.
While 34 percent of respondents reported that cyber resilience was fully embedded within their business strategy, with shared ownership and metrics, 33 percent said it was recognised as a priority but not fully integrated. The remaining 33 percent indicated that responsibility primarily rested with IT or security functions.
The results highlighted a persistent challenge: although resilience is increasingly recognised as a business priority, ownership still remains fragmented.
Rob Brown, Senior Director of Technical Services at Absolute Security, suggested that organisational silos continue to complicate the issue much further. “Resilience isn't just about patching anymore,” he explained, emphasising that protecting individual devices is insufficient when organisations depend on interconnected technologies, teams and services.
Several participants questioned whether the term cyber resilience itself contributes to that disconnect.
One leader argued that organisations should move towards the language of digital resilience and digital safety, making the concept more accessible to employees outside technology functions.
Rather than beginning with technical systems, the recommendation was to understand how employees perform their daily responsibilities, identify their most time-sensitive activities and then work backwards to establish the supporting technology and operational dependencies.
The message here? Resilience should be designed around the business’ outcomes rather than infrastructure alone.
Speaking the boardroom’s language
Security sustained executive investment in cyber resilience is no easy feat; particularly when the benefits of preventative measures are often invisible.
One participant recalled an organisation that had experienced a major cyber attack, invested heavily in recovery and subsequently faced questions from its board about whether continued investment was necessary because no further incidents had occurred.
That example made one thing very clear: it exposed a fundamental contradiction that successful security measures can make their own value harder to demonstrate.
Participants agreed that boards increasingly recognise cyber risk, particularly following high-profile incidents affecting major organisations. However, recognising the threat does not necessarily translate into understanding its operational implications.
The challenge for CIOs and CISOs is to communicate what disruption means for revenue, customer relationships, reputation, and the organisation’s ability to fulfill its own objectives.
Instead of requesting investment through technical specifications or hypothetical worst-case scenarios, leaders were encouraged to demonstrate how specific controls reduce exposure and improve recovery capabilities.
Another recommendation involved communicating successful interventions and near misses. Highlighting incidents that affected comparable organisations, but were avoided internally because of existing controls, can help demonstrate the value of resilience investment.
Most of all, the participants acknowledged that no investment can guarantee absolute protection.
The minimum viable business: How low can you go?
One of the discussion’s most significant themes was the concept of minimum viable business: the essential activities an organisation must maintain during a major disruption.
Reminding themselves that recovery does not mean immediately restoring normal operations, the participants questioned what level of functionality would allow an organisation to continue operating.
Could the business survive with reduced staffing, limited systems or temporary manual processes? More importantly, how long could those arrangements be sustainable?
One leader asked whether organisations were planning for a single day of reduced operations, a week or potentially even an entire month.
Instead of concentrating exclusively on the likelihood of a cyber attack, organisations must understand the consequences of losing particular capabilities and establish acceptable thresholds for disruption.
Participants also highlighted the difficulty of quantifying these risks. Unlike some established areas of operational safety, cybersecurity lacks consistent historical data from which to calculate the probability and consequences of every potential incident.
So, resilience planning requires judgement alongside financial modelling, with business leaders making informed decisions about which risks they can reasonably accept.
People, processes, and the resilience muscle
Technology recovery was only one part of the conversation. Equally important was whether employees could realistically execute business continuity plans under pressure.
Participants questioned the effectiveness of traditional disaster recovery exercises that focus on technical restoration without testing the wider organisation’s ability to function. A system might be successfully restored, for example, while employees remain unable to access alternative premises, understand revised procedures or coordinate with other departments.
Several leaders advocated building organisational muscle memory through regular, practical exercises involving business teams rather than IT alone. Brown reinforced this perspective, describing the importance of rehearsing processes before they become necessary.
“I'd rather have it and not need it than need it and not have it,” he remarked. Repeated exercises can expose overlooked dependencies, including reliance on individual employees who may be unavailable during an incident.
The conversation also addressed the psychological and physical demands placed on employees responding to major disruptions. Leaders described the exhaustion associated with prolonged recovery efforts, alongside the long-lasting emotional effects that serious security incidents can have on staff.
“The way I can describe it is PTSD on the employees in the wake of that,” said one leader.
With hybrid working arrangements and changing workforce expectations, organisations cannot automatically assume that employees will be able to work extended hours or relocate at short notice.
Resilience planning therefore needs to account for workforce capacity, wellbeing and the practical limitations of human endurance.
Metrics matter
How should organisations demonstrate that their cyber resilience strategy is working?
Participants distinguished between lagging indicators, such as incidents experienced and their consequences, and leading indicators that show whether preventative and recovery capabilities remain effective.
Examples included patching performance, the management of privileged accounts, and maintaining agreed security thresholds. The discussion emphasised the importance of tracking these measures consistently and presenting them in a format that boards can understand.
Rather than overwhelming executives with technical reporting, resilience leaders should communicate whether agreed levels of protection are being maintained and where deteriorating performance introduces additional business risk.
One participant suggested that this approach could make resilience reporting comparable to other familiar boardroom issues, such as financial performance or production targets.
However, the absence of universally accepted resilience metrics remains a challenge.
Brown acknowledged the importance of establishing credible measurements that help boards understand what effective resilience actually looks like.
“Boards are balancing pennies and pounds. We’re trying to balance security. But resilience is more than cyber: it’s keeping the business running."
From cyber protection to organisational survival
Towards the end of the discussion, a broader consensus emerged: resilience cannot remain a standalone cybersecurity initiative.
Brown identified three main priorities from the discussion:
- Maintaining continuous communication with the board;
- adopting a broader understanding of digital resilience;
- and recognising the importance of employees responsible for restoring operations.
For CEOs, CIOs, and CISOs, the challenge is to translate these principles into a shared operating model that connects business priorities, technical capabilities and workplace readiness.
Because when disruption becomes unavoidable, the true measure of resilience, as the participants discovered, is not simply how well an organisation protects itself, but how effectively it continues to operate.
This C-Suite Exchange was hosted in partnership with Absolute Security.


Join the community
To join the HotTopics Community and gain access to our exclusive content, events and networking opportunities simply fill in the form below.
